A health platform cannot improvise with its patients' data
CRM implementation, full email architecture, a data protection impact assessment with external legal counsel, and closing down AWS security. Led as fractional CTO.
From problem to solution
- 01 · The challenge
A platform connecting users with aesthetic clinics handles health data, the most sensitive category in data protection law.
On top of that there was a practical problem: nobody was clear on which emails came from where, and cloud storage had been set up quickly during development, as it always is.
- 02 · What we did
We came in as fractional CTO to sort out all three at once.
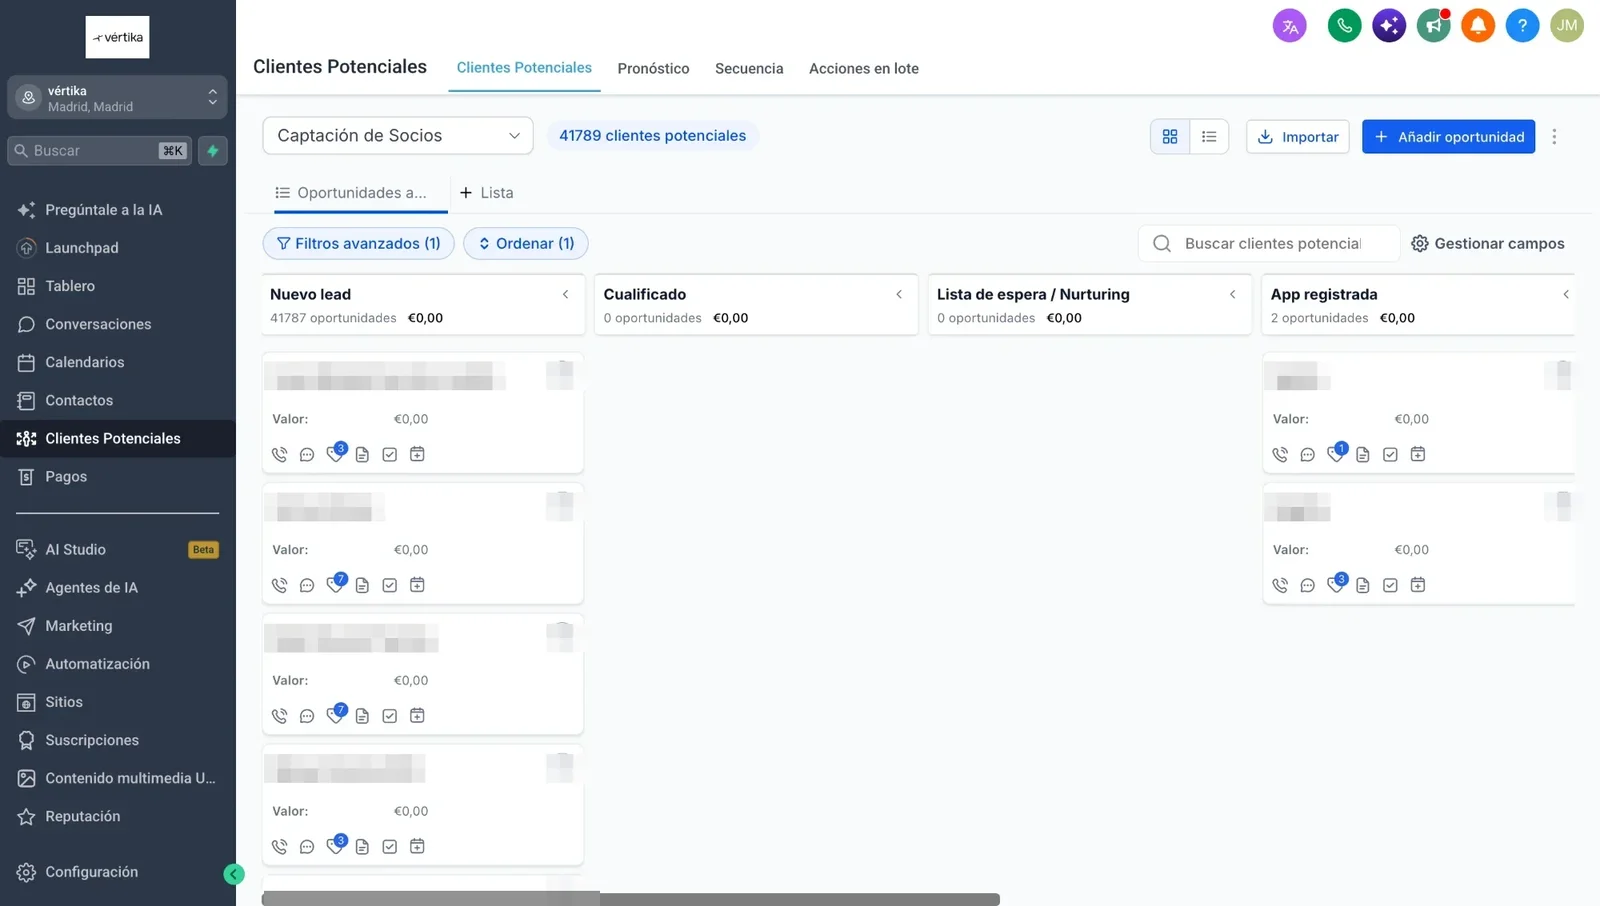
We implemented the CRM in GoHighLevel with its pipelines and campaigns, and designed the email architecture by splitting responsibilities: transactional comes from the product, commercial from the CRM, with 12 branded templates laid out from Figma on top of a catalogue of 39 backend emails. In parallel, alongside legal counsel, we ran the data protection impact assessment (DPIA) and closed down storage security: public access cut off, per-user signed URLs, link revocation and access logging.
How it comes together
Inside the project
Measurable results
Services used on this project
Tech stack used
- GoHighLevel
- SendGrid
- AWS
- Figma


Want something like this for your business?
Tell us about the challenge. In a first call we work out whether we are a good fit and how we could work together.
Ready to work together?
Schedule a meeting or tell us about your project. We respond quickly, no strings attached.